In the landscape of Unix and Linux operating systems, security and multi-user access control are foundational. Every file and directory is bound to a specific owner and group, governed by strict access permissions. Managing these access rights is essential for maintaining system integrity and safeguarding sensitive data. At the heart of this privilege management system lies the chmod command, short for “change mode”. Whether you are a system administrator locking down a server or a developer making a shell script executable, understanding how to use chmod is a vital skill.
Understanding the Anatomy of File Permissions
Before diving into how chmod is used, it is important to understand what it manipulates. When you run a command like ls -l in your terminal, the output reveals a string of characters representing file permissions (e.g., -rwxr-xr--). These permissions are divided into three core classes of users:
- User (u): The individual user who owns the file.
- Group (g): A collection of users who share access rights to the file.
- Others (o): Everyone else on the system who does not fall into the first two categories (often referred to as “world”).
For each of these classes, access is granted through three primary permission types:
- Read (r): Allows viewing the contents of a file or listing the contents of a directory.
- Write (w): Allows modifying, deleting, or creating files within a directory.
- Execute (x): Allows running a file as a program/script or entering and accessing a directory.
Comprehensive breakdowns of these concepts can be explored further in the GeeksforGeeks Linux chmod Guide and the HowtoForge Linux chmod Tutorial.
How to Use chmod: Symbolic Notation
The chmod utility accepts modifications using two distinct approaches: symbolic notation and numeric (octal) notation.
Symbolic notation uses letters and mathematical operators to explicitly add, remove, or set permissions. The syntax typically follows this structure: chmod [who][operator][permission] filename.
- Operators:
+adds a permission.-removes a permission.=sets the exact permission, overriding prior configurations.
- Examples:
- To grant execution permission to everyone for a script named
deploy.sh, you can usechmod +x deploy.sh(which acts as a shorthand fora+x). - To configure strict custom rules—such as giving the owner full control, the group read-write access, and others read-only access—you can write:
chmod u=rwx,g=rw,o=r file.txt.
- To grant execution permission to everyone for a script named
For more examples on structuring symbolic permissions, check out the KodeKloud chmod Guide.
How to Use chmod: Numeric (Octal) Notation
For quick, precise permission adjustments, system administrators frequently prefer numeric notation (also known as octal notation). This method represents permissions using a three-digit (or sometimes four-digit) base-8 number.
Each digit corresponds to a user category in order: Owner, Group, and Others. The value of each digit is calculated by summing the binary-weighted values of the individual permissions:
- Read (r) =
4 - Write (w) =
2 - Execute (x) =
1
By combining these values, you can instantly define a complete permission set:
7(4+2+1) grants Read, Write, and Execute.5(4+0+1) grants Read and Execute.4(4+0+0) grants Read-only.
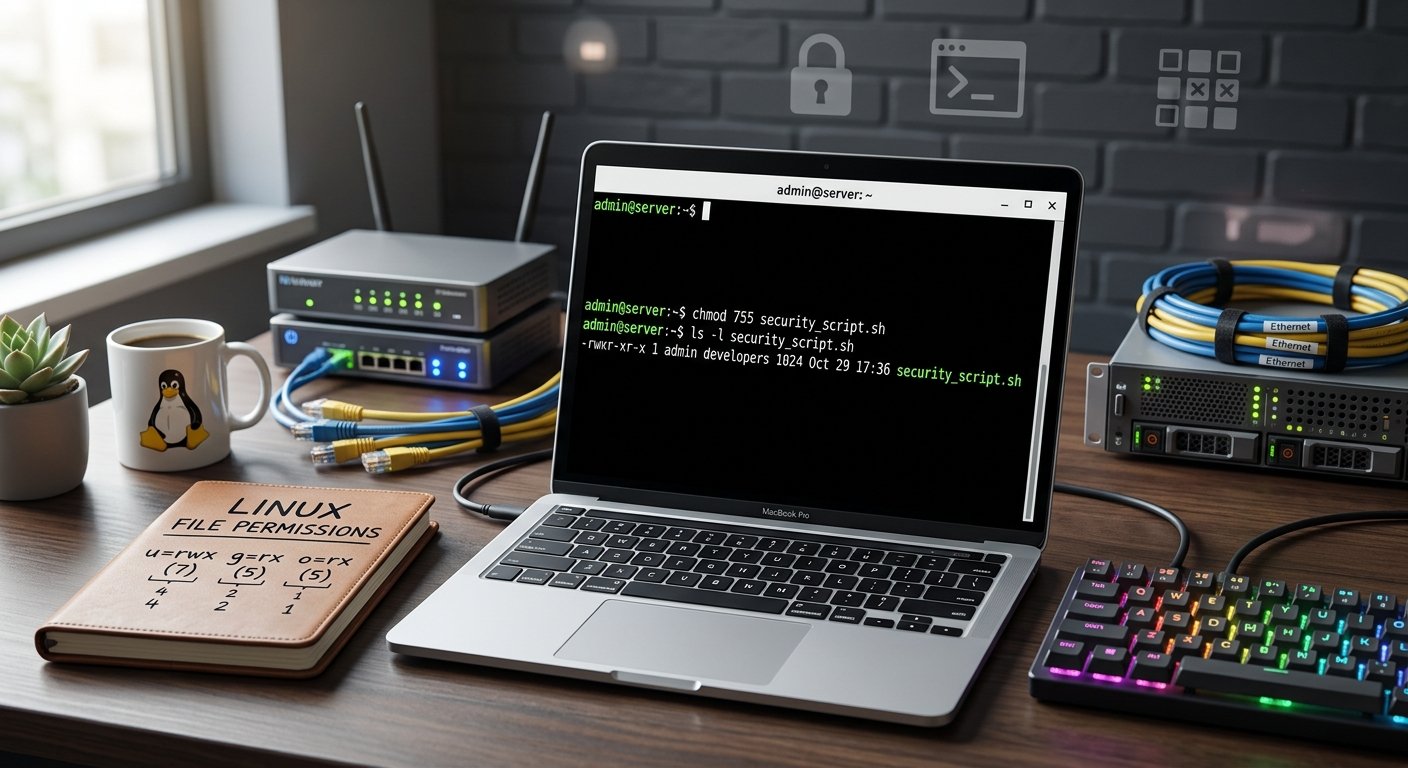
A classic example is chmod 755 script.sh, which gives the owner full access (7), while granting the group and others read and execute privileges (5). Another standard setting for private configuration files is chmod 644 (owner can read and write; group and others can only read). Further explanation of octal mathematics and workflow applications can be found via the FreeCodeCamp Linux Permissions Guide.
Advanced Usage: Recursive Modifications
When dealing with complex folder structures, changing permissions file-by-file is impractical. The chmod command offers the recursive option (-R or --recursive), which applies permission modifications to a target directory and all of its nested contents.
For instance, executing chmod -R 755 /var/www/html will update the entire web directory tree at once. Care must be taken with recursive flags, especially on system-critical directories, to avoid unintended security exposure. For technical specifications and advanced flags like --reference, reference the official Linux Manual Page for chmod.
Conclusion
The chmod command is an indispensable tool within the Linux ecosystem. By mastering both symbolic and numeric notation, administrators and users can fine-tune access controls, ensuring that executables run safely, private files remain shielded, and collaborative directories function smoothly. Whether handling a single script or an entire server architecture, chmod remains the cornerstone of Linux file security.